How to Choose a Test Email Account for QA
A temp inbox handles hands-on sign-up and OTP checks. Tests that run without a person, touch real customer data, or need replies and attachments call for a different kind of test inbox. Here is how to pick the right one for each test.
Quick access
What Is a Test Email Account for QA?
A test email account, or test email address for QA, is an address your team uses to receive and inspect the emails your own application sends. Use a temporary inbox for manual, non-sensitive sign-up and OTP checks. Choose a company mailbox for retained messages, replies, or attachments, and an SMTP sandbox or hosted inbox API when automated tests must inspect email without a person.
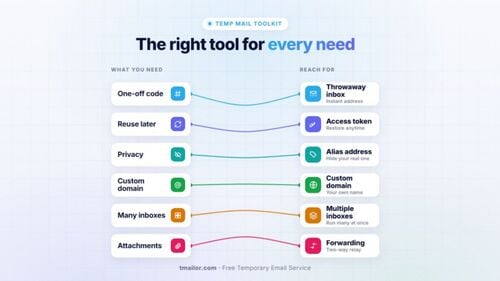
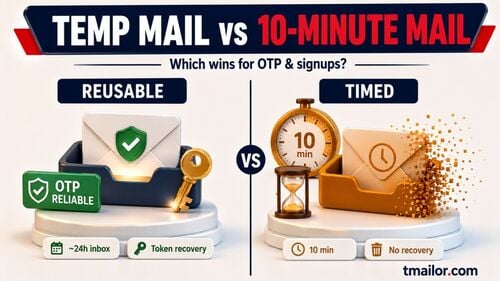
Tmailor runs this blog, so here is where it fits. Tmailor is a free, receive-only temp mail service on the web, Android, iOS, and a Telegram bot. It suits the first case: a person opens an inbox, triggers a sign-up, and reads what arrives. It has no public API, so automated tests cannot create or read Tmailor inboxes. Messages stay about 24 hours from arrival, attachments are not received, and the address cannot send or reply. If you are new to disposable inboxes, start with how temp mail works.
- No email needs to arrive (form validation, fixtures, unit tests): use a reserved example domain.
- A person reads the email and nothing in it is sensitive: a temp inbox is the fastest option.
- Sensitive data, replies, attachments, or evidence you must keep: use an approved company-controlled mailbox; add plus tags only if your mail system and application support them.
- No person watching: use an SMTP catcher if you control the app's outbound mail settings, or a hosted inbox API if the app must send through its normal provider.
Manual vs Automated Email Testing: A Decision Tree
Four questions decide which test email account a check needs: whether an email must arrive at all, whether a person or code reads it, whether it carries sensitive data, and whether you control where the application sends its outbound mail.
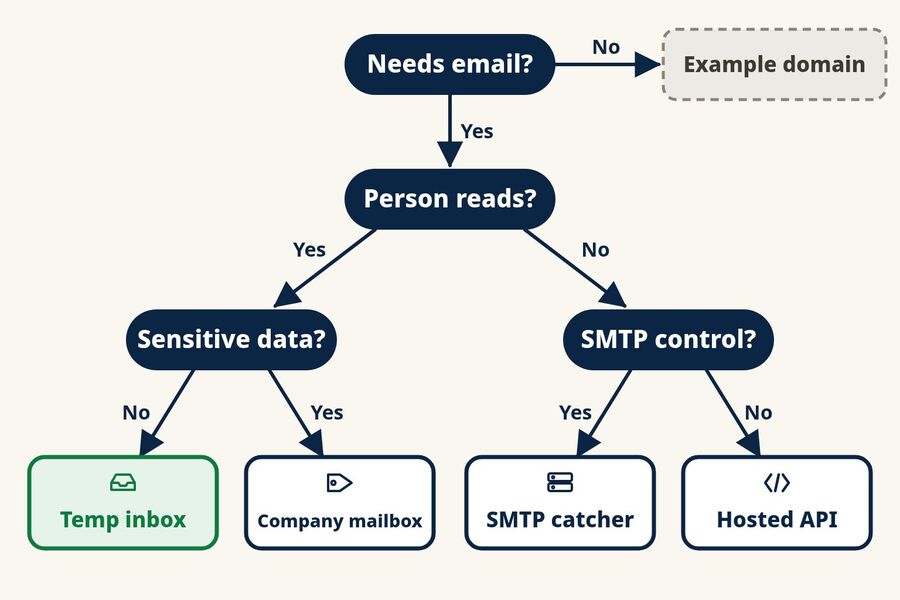
- Does the test need an email to arrive? Format checks, UI states, fixtures, and unit tests usually do not. Use addresses at example.com, example.org, or example.net. Those domains are reserved for documentation and examples, so nothing reaches a real person. Avoid inventing random domains, because someone may own them.
- Will a person read the message during the test? Smoke tests, manual UAT, demos, and exploratory sessions have a human in the loop. Regression suites and CI jobs usually do not.
- If a person reads it, is anything in it sensitive? Real customer records, credentials, regulated data, or messages you must keep as audit evidence do not belong in a temp inbox. Use a company mailbox instead. If the answer is no, a temp inbox is enough.
- If code reads it, can the test environment send its mail to a test SMTP server? If yes, an SMTP catcher captures every message without delivering it. If no, because the app must send through its normal email provider, use a hosted inbox that your tests read through an API.
The table compares the five options side by side.
| Option | Best for | How mail is read | Watch out for |
|---|---|---|---|
| Reserved example domain | Validation, fixtures, negative tests | Not delivered | Cannot test arrival, timing, or content |
| Temp inbox (such as Tmailor) | Smoke tests, manual UAT, demos, exploratory checks | A person in a browser or app | About 24 hours of messages, receive-only, no attachments, no API, not for sensitive data |
| Company-controlled mailbox, optionally with plus tags | Sensitive or long-running flows, replies, attachments, audit evidence | A person, or mailbox access your IT team approves | Tagged addresses share one mailbox, so parallel tests can see each other's mail |
| SMTP catcher or sandbox | Dev, staging, and CI where you control outbound mail settings | Web UI and API | Does not prove delivery over public DNS and MX or inbox placement |
| Hosted inbox API | End-to-end tests through your real sending path | REST API and SDKs | Plan limits, retention, domains, and concurrency vary by vendor |
Which Addresses Should an Email Field Accept or Reject?
Test form validation separately from message delivery. Use a reserved address such as user@example.com for a valid-looking case that never delivers, include an address with a plus tag and one with a subdomain, and add malformed cases such as a missing local part or a missing domain. Keep the expected results aligned with the validator your production system actually uses.
When a Temp Inbox Is Enough
A temp inbox works when a person is checking one flow at a time and the message contains nothing you would mind losing after a day. That is the classic use of a disposable email for QA: you need an email address for testing a form by hand, not a long-lived account. Typical cases are a pre-release smoke test of the sign-up form, a manual UAT pass on a new onboarding email, a sales demo of account creation, or an exploratory session where you try odd inputs and watch what the app sends.
The appeal is speed. There is no account to request from IT and no shared mailbox to clean up. The trade-off is control: you get a short message window, no API, and no attachments.
When You Need an SMTP Catcher or a Hosted Inbox API
Once tests run unattended, the inbox has to be readable by code. Two families of tools cover that need, and they solve different problems.
SMTP catchers and sandboxes replace your app's outbound mail server in a test environment and keep every message for inspection instead of delivering it.
- Mailpit is a free, open-source tool you run yourself. It captures mail by default and offers a web UI and a REST API for integration tests.
- MailHog works the same way but is older. Mailpit's maintainers describe it as no longer maintained, so check its status before adopting it.
- Mailtrap Email Sandbox is a hosted version of the same idea, with SMTP and API access. It is separate from Mailtrap's production sending product.
- Ethereal is a free fake SMTP service used mainly with Nodemailer. Messages are caught for preview and never delivered.
Hosted inbox APIs give tests real addresses on the vendor's domains, so your app sends mail through its normal provider and the test reads the result through an API.
- Mailosaur offers test email addresses, an API, and client libraries that work with frameworks such as Cypress, Playwright, and Selenium. It also covers SMS codes.
- MailSlurp creates inboxes on demand through its API and SDKs. Tests can wait for a message, then pull out codes, links, and attachments.
Vendor features and plans change, so confirm current details on each official site before you commit a test suite to one.
When a Company Mailbox With Plus Tags Is the Better Choice
Plus tags let one company mailbox accept many address variations. Mail to qa+signup or qa+reset at your company domain lands in the qa mailbox, where you can filter it by tag. Google Workspace supports this, and Microsoft documents that plus addressing in Exchange Online is on by default unless an admin turns it off.
Use this route when a flow carries real customer data, runs longer than a day, needs replies or attachments, or produces evidence an auditor may ask for. Keep the limits in mind. Tags are variations of one mailbox, not separate inboxes, so parallel tests can read each other's messages. Some sign-up forms reject the plus sign, and some apps treat tagged variants as the same account. Both behaviors are worth a test case of their own.
How to Run a Manual Sign-Up Test With a Temp Inbox
A manual sign-up test that uses temporary email for testing needs three things: a fresh address, the build you are testing, and a place outside the inbox to record what arrived. Run it only against systems you own or are authorized to test.
- Open an inbox. Create a free temp inbox on the web, or use the Tmailor app or Telegram bot, and copy the address.
- Sign up on your test build. Use the address in your staging or QA environment and note the time you submitted the form.
- Watch for the email. Check which message arrived, the sender name and From address, the subject, and how long it took.
- Complete the step. Click the link or enter the code. Confirm the account changes state once and that reusing the same link fails with a clear message.
- Record the evidence elsewhere. Copy the link, code, timestamps, and a screenshot into your test case. Messages stay about 24 hours from arrival, so the inbox is not your test record.
- Save the Access Token if you will retest. The token reopens the same address later, for example to rerun a password reset. It does not restore messages that have already expired, and a lost token cannot be recovered.
When a session needs several personas at once, such as a free user, a trial user, and an invited teammate, the multiple inboxes view keeps up to five addresses side by side in one browser tab. Each persona gets its own address, so you can see which email belongs to which account.
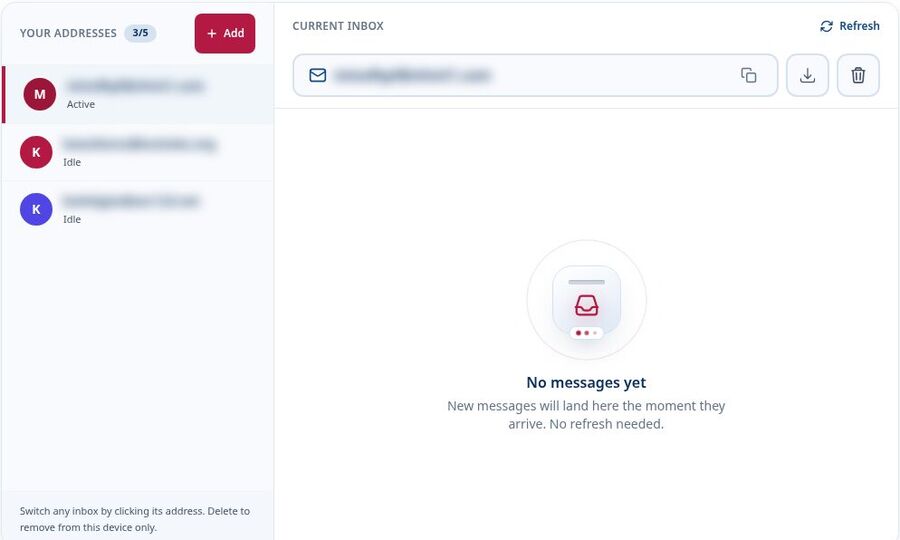
This view is still manual. The inboxes are created by a person in a browser, not provisioned by code, so it does not replace a hosted inbox API for parallel unattended runs.
One Inbox or One Address per Test?
A single shared inbox is fine for a quick smoke check, but it gets noisy fast. Once several tests run at the same time, similar subject lines make it hard to tell which email belongs to which script, and debugging turns into guesswork.
One address per test case solves that. Logs, screenshots, and emails line up, and a missing message points to one scenario instead of all of them. The guide to running multiple temp mail inboxes covers that workflow in more detail.
Some journeys need the same address again days later, such as a trial that converts or a user who comes back after churning. A reusable temp mail address keeps the address available through its Access Token, but not the mail. Store the links and codes you need as each step runs, and move any step that depends on older messages to a company mailbox.
| Pattern | Best use | Main risk |
|---|---|---|
| Shared inbox | Smoke checks and short manual sessions | Hard to match messages to tests once runs overlap |
| Per-test address | Multi-step sign-up and onboarding cases | More addresses to track and retire |
| Reusable persona address | Trial-to-paid, reactivation, and return visits | Messages still expire after about 24 hours; a lost token means a lost address |
What to Check in Sign-Up and Onboarding Emails
Start with an inventory of every email the journey can send, then decide what each test should assert. Teams often discover extra emails only when they show up mid-test, after a growth experiment or a security change added one nobody wrote down.
Emails in a Typical Sign-Up Journey
- Verification link or one-time code
- Welcome email and any quick-start sequence
- Magic-link sign-in
- Password reset
- Email address change, sent to both the old and the new address
- New device or new location security alert
- Reminders for sign-ups that were never finished
For each one, write down the trigger, the expected timing, and the conditions that change it, such as plan, region, or language. Set the allowed delivery window from your product's documented requirement rather than assuming a universal threshold; an immediate verification message and a scheduled welcome sequence need different expectations. Once those expectations exist, every test has something concrete to check against.
What to Assert in Each Test Email
- Sender and recipient: From name and address, Reply-To, and the exact To address.
- Subject and body: both the HTML and plain-text versions, with correct names, plan details, and language.
- Links: the destination and whether it points to the right environment. A staging email that links to production is a real bug.
- Codes: format, length, expiry copy, and whether the stated expiry matches what the server enforces.
- Timing: how long the message took to arrive after the trigger.
- Attachments: if a flow sends a PDF or invoice, test it in a company mailbox or a testing tool. Tmailor does not receive attachments.
One caution on rendering. A temp inbox shows how one web viewer displays your HTML. It does not tell you how the same email looks in Gmail, Outlook, Apple Mail, dark mode, or a small phone screen, so plan separate rendering checks if those matter.
Email Change and Account Recovery Flows
Recovery flows break in quieter ways than sign-up. Check that an email change sends a confirmation to the new address and a notice to the old one, that a used reset link cannot be reused, that an older reset link stops working after a newer one is sent, and that a link opened on a second device lands the user in a sensible state. OTP flows deserve a separate risk review; the OTP risk checklist for QA and UAT covers metrics, resend windows, and ownership.
How to Test OTP and Verification Edge Cases
Test OTP and verification flows against delayed delivery, resends, expired and incorrect codes, and links opened on another device. Each case should check both the server result and the message shown to the user. Run these tests only on systems you own or are authorized to test. Good OTP tests break the flow on purpose:
- Slow arrival: wait before checking the inbox and confirm the UI explains what is happening and offers a clear way to resend.
- Resend behavior: request a second code and check whether the first one is invalidated or still accepted.
- Expiry: enter a code after its stated lifetime and confirm the error message matches what happened.
- Wrong code: confirm the attempt limit and the cooldown copy make sense to a person.
- Cross-device magic links: request a link on a laptop, open it on a phone, and check where the user ends up.
For a broader view of which codes reach a temp inbox and which do not, see this guide on temp mail for OTP codes.
If your product rejects disposable email domains on purpose, test that path directly. Confirm the rejection message is clear and that a real or company-controlled address still completes sign-up. Do not cycle through other temp domains to get past the block, on your own product or anyone else's. Confirming the block works is the test; defeating it is not. This explainer on why websites block temp mail domains covers the reasons behind those filters.
What Changes When Email Tests Run Unattended
When no person is watching, the test needs an inbox it can read through code. That means an SMTP catcher's API or a hosted inbox API. Tmailor is not that tool: it has no public API, no polling endpoint, and no webhook.
A few habits keep unattended email tests stable, whichever tool you choose:
- Give every test run its own address and a correlation ID, so a late email from an earlier run cannot satisfy the wrong assertion.
- Use a dedicated wait for email arrival with sensible backoff, separate from the overall test timeout, and log how long each message took.
- Match the exact message by recipient and subject instead of reading "the latest email."
- Mask codes and magic links in CI logs, since logs often outlive the inbox.
Also be clear about what a passing test proves. "The app generated and handed off the email," "a hosted test domain received it over public email infrastructure," and "Gmail placed it in the inbox, not spam" are three different facts. An SMTP catcher proves the first, a hosted inbox API proves the first two, and neither proves the third. For pipeline setup on GitHub Actions, GitLab CI, and CircleCI, see the guide to email testing in CI/CD pipelines.
Keep Test Data Safe and Stay Within the Rules
Use synthetic identities and non-sensitive content in temporary test inboxes, and run sign-up tests only against systems you own or are authorized to assess. Keep QA accounts out of production analytics, respect rate limits, and move regulated data, credentials, attachments, and retained evidence to approved company-controlled systems.
- No real data in a temp inbox. Never route real customer records, credentials, API keys, or regulated data to a temp mail address. Use synthetic users with obviously fake names.
- Test only what you are allowed to test. Run sign-up tests against your own product or a system you are authorized to test, and respect that service's rate limits and terms. Do not use temp mail to create accounts in bulk on third-party sites. Volume and load testing belong in your own staging environment, with an SMTP catcher or a hosted inbox API.
- Keep QA traffic out of production numbers. Label test accounts clearly and exclude them from analytics and growth dashboards. Avoid sending large volumes of test mail from your production sending domain, where bounces and complaints can hurt its reputation.
- Write down the policy. State which flows may use a temp inbox, which need a company mailbox, how long test data is kept, and who has access. Security and compliance reviews go faster when the boundaries are already on paper.
When security asks how a provider handles data, look at what it collects, how long it keeps messages, and how access works. This overview of temp mail and online privacy covers those questions from the user side. The decision about which flows may use disposable inboxes still belongs to your own legal, privacy, and security teams.
Limits to Plan Around
Tmailor fits short manual checks of non-sensitive inbound email. Before choosing it, decide whether the workflow needs outbound actions, attachments, automation, long-lived evidence, or durable address recovery. Any of those requirements calls for a company-controlled mailbox or a specialist testing tool; the checklist below explains why.
- Tmailor is receive-only. It can check inbound sign-up, verification, and OTP mail, but not reply flows or anything that sends from the address.
- Tmailor does not receive attachments, so invoice, contract, or document-delivery emails need a company mailbox or a testing tool.
- Messages stay about 24 hours from arrival. Export the links, codes, and timestamps that a longer investigation will need.
- An Access Token reopens an address, not expired messages, and a lost token cannot be recovered.
- Tmailor has no public API. Unattended inbox reading needs an SMTP catcher or a hosted inbox API.
- Some services block disposable email domains. If a flow you test does this on purpose, validate it with a real or company-controlled address.
Frequently Asked Questions
Can I use a temporary email address for QA testing?
Yes, for manual tests where a person reads the email and nothing in it is sensitive. A temp inbox works well for smoke tests, manual UAT, and demos of sign-up and OTP flows. It is the wrong choice for real customer data, attachments, replies, messages you must keep longer than about 24 hours, or tests that run without a person.
Can automated tests read a Tmailor inbox through an API?
No. Tmailor has no public API, so scripts cannot create or poll Tmailor inboxes. Use an SMTP catcher such as Mailpit or Mailtrap Email Sandbox when you control the app's outbound mail settings, or a hosted inbox API such as Mailosaur or MailSlurp when the app must send through its normal provider.
What is the difference between a test email account and an SMTP sandbox?
A test email account, or test mailbox, is a receiving address your application can send to, where a person or a test inspects the delivered message. An SMTP sandbox instead replaces the app's outbound mail server and captures the message before public delivery. A receiving mailbox tests more of the sending path, but neither option by itself proves Gmail or Outlook inbox placement.
Should each QA test use a different email address?
Usually, yes. One address per test case keeps logs, screenshots, and emails aligned and stops one test from reading another test's message. A shared inbox is acceptable for a quick smoke check, but it becomes hard to debug once several tests run at the same time.
Can I reuse the same Tmailor address for another test?
Yes, if you saved its Access Token. The token reopens the same address on any device, which helps with retests and multi-day journeys. It does not bring back messages older than about 24 hours, and a lost token cannot be recovered, so record the links and codes you need as each step runs.
When should QA use a company mailbox instead of temporary email?
Use a company mailbox when the email contains real customer data or credentials, when the flow needs replies or attachments, when you must keep the message as audit evidence, or when a product deliberately blocks disposable domains. Third-party identity providers and production migrations also usually need real, company-controlled addresses.
Can plus-addressing create separate test accounts?
It creates address variations, not separate inboxes. Mail to qa+one and qa+two at your domain arrives in the same qa mailbox, so tests share message history. Your application may accept the variants as different accounts, reject the plus sign, or normalize them to one user. Treat that behavior as a test case rather than an assumption.
Why did a verification email not arrive in the test inbox?
The most common causes are a sending error in the app, a delay at the email provider, a rate limit on repeated requests, a typo in the address, or a filter that rejects disposable domains. Check your app's mail logs first, then retry once with a company-controlled address to see whether the problem follows the address or the flow.
Can a temporary inbox test attachments, replies, or email deliverability?
Not with Tmailor. It does not receive attachments and cannot send or reply. Receiving a message in a temp inbox also does not show whether Gmail or Outlook would place it in the inbox or in spam. Use a company mailbox for attachments and replies, and a dedicated deliverability or seed-testing service for inbox placement.
Can test sign-ups with temporary email skew our analytics?
They can if the traffic is not labeled. Mark every test account clearly, for example with a naming convention or a test flag, and exclude those accounts from production dashboards and growth reports. Running tests in a separate staging environment keeps most of that traffic out of real numbers in the first place.
Picking the Right Test Inbox
Choose the inbox according to what the test must prove. Use a reserved example domain when delivery is unnecessary, a temporary inbox for manual non-sensitive checks, a company mailbox for retained or sensitive journeys, an SMTP catcher when you control outbound settings, and a hosted inbox API for unattended end-to-end tests.
For the manual cases, open a temp inbox and start with the sign-up flow you ship next. Temp mail has plenty of practical uses beyond QA as well.

Marcus Lee writes Tmailor's step-by-step guides — signing up to apps and platforms with temp mail, using the mobile app and Telegram bot, custom domains, reusing addresses, and getting the most out of disposable email day to day.